Zero Trust Security Model Explained (2026): Architecture, Principles & Implementation Guide
Cybersecurity is changing faster than ever in 2026. Traditional firewalls and perimeter-based security systems are no longer enough because modern businesses now operate across cloud platforms, remote work environments, mobile devices, SaaS applications, APIs, and AI-powered systems. Attackers no longer need to break through a single company firewall to access sensitive information. Instead, they target identities, cloud applications, weak endpoints, stolen credentials, and poorly secured remote connections. This is exactly why the Zero Trust Security Model has become one of the most important cybersecurity strategies worldwide. Governments, enterprises, banks, healthcare companies, and technology organizations are rapidly moving toward Zero Trust Architecture because the old “trust but verify” model no longer works effectively in modern digital environments. The core idea behind Zero Trust is simple but powerful: never trust anyone or anything by default, even if they are inside the network. Every user, device, application, and request must continuously prove legitimacy before gaining access to resources.
- Zero Trust Security Model Explained (2026): Architecture, Principles & Implementation Guide
- What Is the Zero Trust Security Model?
- Why Traditional Security Models Are Failing
- The Core Philosophy Behind Zero Trust
- Zero Trust Architecture Explained
- The Five Pillars of Zero Trust Security
- Identity Is Becoming the New Security Perimeter
- Zero Trust Network Access (ZTNA) Explained
- Microsegmentation in Zero Trust Architecture
- How AI Is Changing Zero Trust Security in 2026
- Real-World Zero Trust Security Examples
- Benefits of Zero Trust Security
- Challenges of Implementing Zero Trust
- How to Implement Zero Trust Security
- Zero Trust and Cloud Security
- The Future of Zero Trust Security
- Conclusion
- FAQs
🚀 Discover the latest platforms transforming workflow management in our article on Top AI Tools for Business Automation.
What Is the Zero Trust Security Model?
The Zero Trust Security Model is a cybersecurity approach where no user, device, application, or network connection is trusted automatically. Every access request must be verified continuously based on identity, device security, behavior, location, risk level, and other contextual factors. Traditional security systems assumed that users inside a corporate network were safe and trustworthy. Zero Trust completely removes this assumption. Instead of trusting internal users automatically, Zero Trust validates every request individually. This approach dramatically reduces the risk of unauthorized access, insider threats, credential theft, ransomware attacks, and lateral movement inside enterprise networks. The concept became popular after organizations realized that modern cyberattacks often bypass perimeter-based defenses entirely. Today, Zero Trust is considered one of the most effective cybersecurity frameworks for cloud computing, hybrid work, remote access, IoT devices, AI systems, and distributed enterprise environments. According to recent NIST and NSA implementation frameworks released in 2025 and updated through 2026, Zero Trust is now evolving from a theoretical concept into detailed enterprise implementation strategies. discover the 10 Best Free AI Tools that every student in India should start using right now 
Why Traditional Security Models Are Failing
Traditional cybersecurity models were designed during a time when employees worked mainly from office networks using company-owned devices. Security teams focused on protecting the network perimeter using firewalls, VPNs, and internal trust zones. Once users entered the network, they often received broad access to systems and applications. This model worked reasonably well when business environments were centralized. However, modern organizations now operate very differently. Employees work remotely, applications run across multiple cloud platforms, and sensitive data moves continuously between users, APIs, mobile devices, and SaaS services. Cybercriminals exploit this complexity by stealing credentials, hijacking sessions, attacking cloud workloads, and moving laterally across networks once initial access is gained. Traditional perimeter-based defenses struggle because there is no longer a single perimeter to protect. This is one of the main reasons NIST and modern cybersecurity frameworks emphasize identity-focused and context-aware security models instead of relying solely on network boundaries. Explore how multi-agent AI systems are transforming enterprise automation, customer support, and data analysis.
The Core Philosophy Behind Zero Trust
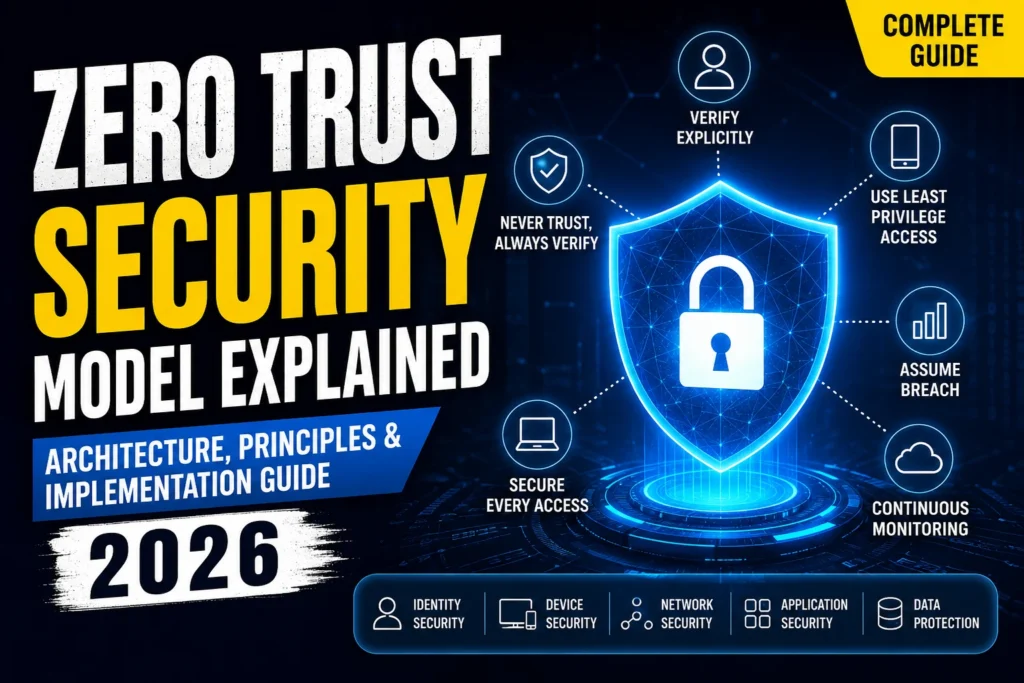
The Zero Trust philosophy is built around one major principle: “Never Trust, Always Verify.” This means every access request must be authenticated, authorized, and continuously validated regardless of where the request originates. Whether a user is inside the office, working remotely, or accessing systems through cloud applications, the system treats every request as potentially risky until proven safe. Zero Trust also follows the principle of least privilege access, meaning users and devices only receive the minimum permissions required to perform specific tasks. Instead of giving broad network access, Zero Trust limits exposure by granting highly controlled and segmented access to resources. Another important concept is continuous monitoring. Security systems constantly analyze user behavior, device health, login patterns, and risk signals to detect suspicious activity in real time. This approach significantly reduces attack surfaces and minimizes the damage caused by compromised accounts or insider threats.
Zero Trust Architecture Explained
Zero Trust Architecture, often called ZTA, refers to the technical framework used to implement Zero Trust principles across an organization’s infrastructure. Instead of relying on a single security layer, ZTA combines multiple security technologies working together continuously. According to NIST’s Zero Trust Architecture guidance and implementation frameworks, Zero Trust systems typically focus on several key pillars including identity management, device security, application protection, network segmentation, workload security, and data protection. The architecture continuously evaluates trust levels based on identity verification, device posture, behavioral analysis, policy enforcement, and risk assessment. Modern Zero Trust environments often integrate technologies such as Multi-Factor Authentication (MFA), Endpoint Detection and Response (EDR), Zero Trust Network Access (ZTNA), Identity and Access Management (IAM), microsegmentation, cloud security platforms, and AI-powered threat analytics. Instead of trusting network locations, the architecture focuses primarily on identity, context, and policy enforcement.
The Five Pillars of Zero Trust Security
Modern Zero Trust frameworks usually focus on five major security pillars. The first pillar is identity security, which ensures that every user and service is authenticated properly using methods like MFA, biometrics, passwordless authentication, and identity verification systems. The second pillar is device security, where organizations verify whether devices meet security standards before allowing access. The third pillar focuses on network security through segmentation and controlled connectivity instead of broad internal access. The fourth pillar protects applications and workloads using policy-based access controls and runtime monitoring. The fifth pillar focuses on data security by encrypting sensitive information and controlling how data is accessed, shared, and stored. Recent NIST implementation models and NSA Zero Trust guidelines strongly emphasize these pillars because modern attacks often target identities, cloud workloads, APIs, and endpoints instead of traditional networks alone.
Identity Is Becoming the New Security Perimeter
One of the biggest changes happening in cybersecurity is the shift from network-based trust to identity-based trust. In traditional systems, being connected to the company VPN often implied trust. In Zero Trust environments, identity becomes the primary security control. Every user, device, API, service account, and even AI agent must continuously verify identity before accessing resources. This shift is becoming even more important in 2026 because organizations are increasingly deploying AI-powered systems, autonomous agents, and machine-to-machine communication platforms. Security experts now emphasize “identity-first connectivity” where authentication and authorization occur before network access is even established. Recent cybersecurity discussions and community analysis highlight that Zero Trust is evolving beyond simple VPN replacement into a complete identity-native connectivity model.
Zero Trust Network Access (ZTNA) Explained
Zero Trust Network Access, commonly called ZTNA, is one of the most important technologies used in Zero Trust implementations. Traditional VPNs often provide broad network access once users authenticate successfully. ZTNA works differently. Instead of granting access to the entire network, it connects users only to specific applications or services they are authorized to use. Access decisions are made dynamically based on user identity, device health, location, behavior, and policy conditions. This greatly reduces lateral movement opportunities for attackers because users never gain unrestricted network visibility. ZTNA solutions are rapidly replacing legacy VPN systems in enterprises because they offer stronger segmentation, reduced attack surfaces, and better visibility into user activity.
Microsegmentation in Zero Trust Architecture
Microsegmentation is another critical concept in Zero Trust security. Traditional networks often allow broad communication between internal systems, making it easier for attackers to move laterally after gaining initial access. Microsegmentation divides environments into smaller isolated zones with strict access controls between them. Even if attackers compromise one system, they cannot move freely across the network because every connection requires separate authorization. Cloud-native environments, Kubernetes workloads, APIs, and modern microservices architectures increasingly rely on microsegmentation to strengthen security. Recent research into Zero Trust implementation for cloud-native and microservices environments highlights how identity federation and fine-grained policy enforcement are becoming essential for securing distributed applications.
How AI Is Changing Zero Trust Security in 2026
Artificial intelligence is significantly influencing modern Zero Trust implementations. AI-powered systems now help organizations detect anomalies, analyze user behavior, identify suspicious activity, and automate policy enforcement in real time. AI can analyze massive amounts of security telemetry much faster than human analysts, making it easier to detect unusual login behavior, compromised accounts, insider threats, and advanced cyberattacks. However, AI also creates new security risks because autonomous agents and large language models often require access to sensitive data and enterprise systems. Security researchers and industry experts now emphasize that Zero Trust principles are essential for securing AI environments safely. AI systems themselves must operate under strict identity verification, policy enforcement, and continuous monitoring controls.
Real-World Zero Trust Security Examples
Many organizations already use Zero Trust principles in real-world environments. Cloud platforms such as Microsoft Azure, Google Cloud, and AWS implement identity-focused security controls combined with continuous monitoring and policy enforcement. Banks use Zero Trust frameworks to secure customer accounts, transactions, and financial systems. Healthcare organizations use Zero Trust to protect patient records and comply with data privacy regulations. Remote work environments increasingly rely on ZTNA platforms instead of traditional VPNs. Governments and defense organizations are also adopting Zero Trust aggressively because critical infrastructure systems require stronger protection against nation-state cyberattacks. In 2025 and 2026, NIST released extensive Zero Trust implementation frameworks demonstrating multiple real-world enterprise architecture examples using commercially available technologies.
Benefits of Zero Trust Security
Zero Trust offers several major advantages compared to traditional cybersecurity models. One of the biggest benefits is reduced attack surface because users only receive limited access instead of broad network permissions. Continuous authentication and monitoring improve visibility into suspicious behavior and insider threats. Zero Trust also strengthens cloud security because policies follow identities and workloads rather than depending on network locations. Organizations gain stronger protection against ransomware, credential theft, phishing attacks, and lateral movement inside networks. Another major advantage is improved compliance because Zero Trust frameworks support better access control, audit logging, and data protection policies. As hybrid work environments continue growing globally, Zero Trust also provides more secure remote access compared to legacy VPN-based architectures.
Challenges of Implementing Zero Trust
Although Zero Trust provides major security benefits, implementation is not simple. Many organizations still operate legacy infrastructure that was never designed for identity-driven security models. Integrating older applications with modern authentication systems can be technically complex and expensive. Organizations also face challenges related to user experience because excessive authentication requirements can create friction for employees. Another major challenge is visibility. Many companies do not fully understand their assets, users, APIs, devices, and cloud workloads, making policy enforcement difficult initially. Security skill shortages also slow adoption because implementing Zero Trust requires expertise across identity management, cloud security, networking, policy orchestration, and threat detection. Recent NSA implementation guidance stresses that Zero Trust should be approached gradually through phased maturity models instead of attempting massive overnight transformations.
How to Implement Zero Trust Security
Successful Zero Trust implementation usually begins with visibility and assessment. Organizations first identify users, devices, workloads, applications, APIs, and sensitive data across environments. The next step involves strengthening identity systems using MFA, Single Sign-On (SSO), device posture verification, and identity governance. After identity controls are established, organizations gradually implement segmentation, policy-based access control, continuous monitoring, and behavior analytics. Modern implementation strategies also focus heavily on endpoint security, cloud workload protection, API security, and AI-powered threat detection. Security experts recommend phased deployment approaches where organizations prioritize high-risk assets first before expanding Zero Trust policies across broader environments. NIST’s latest implementation frameworks now provide detailed technical models and real-world reference architectures that organizations can follow during deployment.
Compare multi-cloud vs hybrid cloud in 2026. Learn the differences, benefits, security, costs, scalability, and best cloud strategy for startups and enterprises.
Zero Trust and Cloud Security
Cloud computing is one of the biggest reasons Zero Trust adoption is accelerating globally. Traditional perimeter security becomes ineffective when applications and data are distributed across multiple cloud platforms. Zero Trust security models work much better in cloud environments because policies are identity-driven rather than location-driven. Cloud-native Zero Trust environments continuously validate user sessions, workloads, APIs, and service identities regardless of where resources are hosted. Multi-cloud architectures, SaaS applications, remote workers, and third-party integrations all benefit significantly from Zero Trust approaches because access decisions remain consistent across distributed environments.
The Future of Zero Trust Security
The future of Zero Trust security is moving toward fully adaptive and intelligent security ecosystems. AI-driven policy enforcement, behavioral analytics, passwordless authentication, decentralized identities, continuous risk scoring, and automated response systems will become increasingly common. Security experts also expect Zero Trust principles to expand deeply into IoT environments, machine identities, AI agents, and edge computing platforms. Researchers are actively studying how Zero Trust models can secure AI ecosystems, autonomous systems, and next-generation digital infrastructures safely. Recent academic and industry research indicates that Zero Trust is evolving from a network security framework into a broader identity-centric operational model for securing every digital interaction.
Conclusion
The Zero Trust Security Model is no longer just a cybersecurity trend. It is rapidly becoming the foundation of modern enterprise security architecture in 2026. Traditional perimeter-based defenses cannot effectively protect today’s distributed cloud environments, remote workforces, AI-powered systems, APIs, and hybrid infrastructures. Zero Trust changes the security approach completely by eliminating implicit trust and continuously verifying every user, device, application, and request. Although implementation can be complex, organizations adopting Zero Trust gain stronger protection against ransomware, credential theft, insider threats, cloud attacks, and modern cyber risks. As digital transformation accelerates globally, Zero Trust Architecture will continue evolving into one of the most important cybersecurity strategies for protecting future enterprise environments.
FAQs
What is the Zero Trust Security Model?
The Zero Trust Security Model is a cybersecurity approach where no user, device, or application is trusted automatically. Every access request must be continuously verified before access is granted.
Why is Zero Trust important in 2026?
Zero Trust is important because modern businesses use cloud platforms, remote work, AI systems, and distributed applications that traditional perimeter-based security cannot protect effectively.
What are the core principles of Zero Trust?
The main principles include never trust always verify, least privilege access, continuous monitoring, identity verification, and microsegmentation.
What is Zero Trust Network Access (ZTNA)?
ZTNA is a security approach that grants users access only to specific applications or services instead of exposing the entire network like traditional VPNs.
Is Zero Trust suitable for small businesses?
Yes, small businesses can implement Zero Trust gradually using MFA, identity management, endpoint protection, and cloud security tools to improve cybersecurity significantly.